Vantage Sherlock Walkthrough
Network pcap analysis of a cloud breach: ffuf fuzzing, OpenStack credential theft, Swift container enumeration and user data exfiltration.
HTB Sherlock — Vantage
Solved Vantage from Hack The Box!
| Field | Value |
|---|---|
| Category | Network Analysis |
| Difficulty | — |
| Status | ✅ Completed |
| Date | 2026-01-07 |
| Hosts | controller, web-server pcap files |
| Stack | Suricata, zeek, WireShark, tshark |
Scenario
A small company moved some of its resources to a private cloud installation. The developers left the redirect to the dashboard on their web server. The security team got an email from the alleged attacker stating that the user data was leaked. It is up to you to investigate the situation.
Q1 — What tool did the attacker use to fuzz the web server ? (Format- include version e.g, nmap@7.80)
Answer ffuf@2.1.0
tshark -r web-server.2025-07-01.pcap -Y "http.request" -T fields -e ip.src -e ip.dst | uniq -c | sort -un

   1 10.116.0.3      10.116.0.4
   2 184.105.247.252 157.230.81.229
 302 117.200.21.26   157.230.81.229
3394 117.200.21.26   157.230.81.229
tshark -r web-server.2025-07-01.pcap -Y "http.request" -T fields -e ip.src -e ip.dst -e http.user_agent | sort | uniq -c | sort -un
      1 10.116.0.3      10.116.0.4      Fuzz Faster U Fool v2.1.0-dev
      2 184.105.247.252 157.230.81.229  Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/109.0.0.0 Safari/537.36 Edg/109.0.1518.70
     20 10.116.0.3      10.116.0.4      Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/137.0.0.0 Safari/537.36
   3695 117.200.21.26   157.230.81.229  Fuzz Faster U Fool v2.1.0-dev
Notes:
At first I run tshark command http.request communications on the pcap file. We saw 3394 http.requests from SourceIP: 117.200.21.26 to 157.230.81.229 Probably fuzzing. Lets investigate further. The question says to find the tool that the attacker use. Lets check the User-Agent . On the second tshark command we find Fuzz Faster U Fool v2.1.0-dev
Q2 — Which subdomain did the attacker discover?
Answer cloud
tshark -r web-server.2025-07-01.pcap -Y "http and ip.src==117.200.21.26" -T fields -e http.host | sort | uniq -c | sort -n

      2 www3.vantage.tech
      2 www.blog.vantage.tech
      2 www.dev.vantage.tech
      2 www.forum.vantage.tech
      2 www.m.vantage.tech
      2 www.test.vantage.tech
      2 www.vantage.tech
     21 cloud.vantage.tech
Notes:
I used on tshark to filter http and ip.src and extract the fields -e http.host We found that cloud.vantage.tech have more occurrences so the answer is cloud
Q3 — How many login attempts did the attacker make before successfully logging in to the dashboard?
Answer 3
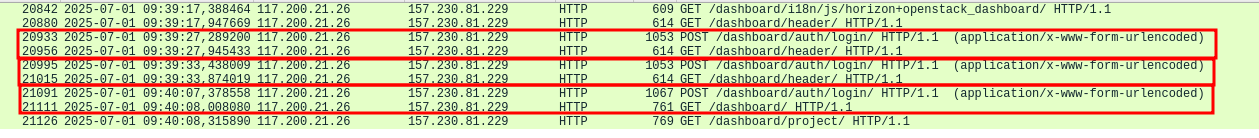
http && ip.addr == 117.200.21.26 && http.referer == http://cloud.vantage.tech/dashboard/auth/login/
Notes:
As we see 3 times try to login. The 3rd was succeed because we saw /dashboard/project/
Q4 — When did the attacker download the OpenStack API remote access config file? (UTC)
Answer 2025-07-01 09:40:29
_path=="http" | id.orig_h==117.200.21.26 | cut ts, uid, method, uri, referrer, resp_filenames

Notes:
Using Zui/Zeek http logs, filtered by attacker IP 117.200.21.26 and inspected
the resp_filenames field. Found that at 2025-07-01 09:40:29 UTC the attacker
downloaded admin-openrc.sh from /dashboard/project/api_access/openrc/.
admin-openrc.sh is an OpenStack credentials file containing API endpoint URLs, project ID, username, and password. Possession of this file gives the attacker
full programmatic access to the OpenStack cloud infrastructure via CLI or API,
bypassing the web dashboard entirely.
Q5 — When did the attacker first interact with the API on controller node? (UTC)
Answer 2025-07-01 09:41:44
_path=="http" | cut ts, method, uri
Notes:
After downloading admin-openrc.sh at 09:40:29, the attacker used the credentials to authenticate directly against the OpenStack API. At 2025-07-01 09:41:44 UTC the first API interaction was observed — a GET request to the compute/nova API endpoint, approximately 75 seconds after the openrc file was downloaded.
This confirms the attacker transitioned from web dashboard browsing to direct API access using the stolen credentials — a significant escalation giving them programmatic control over the cloud infrastructure
Q6 — What is the project id of the default project accessed by the attacker?
Answer 9fb84977ff7c4a0baf0d5dbb57e235c7
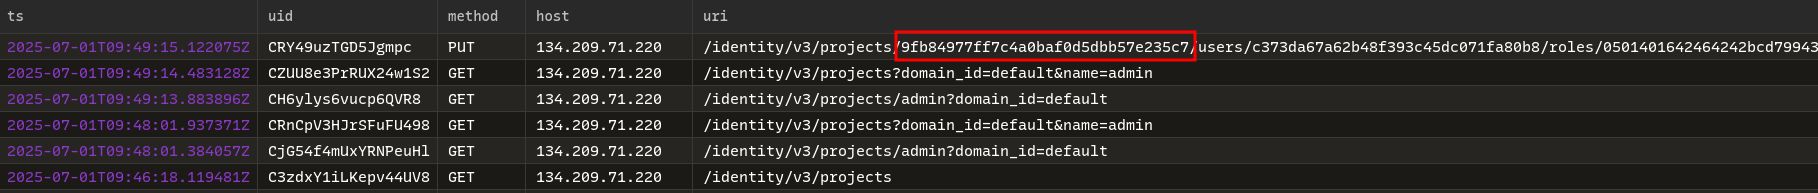
_path=="http" | id.orig_h==117.200.21.26 | cut ts, uid,method, host, uri | projects
Notes:
At 09:48:01 UTC the attacker queried the Identity API for the default admin project:GET /identity/v3/projects?domain_id=default&name=admin
The project ID 9fb84977ff7c4a0baf0d5dbb57e235c7 was returned and confirmed visible in the PUT request at 09:49:15 UTC where the attacker used it to assign admin role to backdoor account jellibean.
Q7 — Which OpenStack service provides authentication and authorization for the OpenStack API?
Answer keystone
Notes:
According to google: **Keystone** is an OpenStack service that provides API client authentication, service discovery, and distributed multi-tenant authorization by implementing OpenStack's Identity API.
Q8 — What is the endpoint URL of the swift service?
Answer http://134.209.71.220:8080/v1/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7
Notes:
Swift endpoint URL found by filtering port 8080 traffic in Zui. All object storage requests used host 134.209.71.220:8080 with path /v1/AUTH_[project_id] confirming the full endpoint URL:
http://134.209.71.220:8080/v1/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7
Q9 — How many containers were discovered by the attacker?
Answer 3 -- dev-files, emlpoyee-data, user-data
tshark -r controller.pcap --export-objects http,./extracted/

cat ./extracted/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7%3fformat=json | jq .cat AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7%3fformat=json | jq .
[
  {
    "name": "dev-files",
    "count": 0,
    "bytes": 0,
    "last_modified": "2025-07-01T04:22:36.008860",
    "storage_policy": "Policy-0"
  },
  {
    "name": "employee-data",
    "count": 0,
    "bytes": 0,
    "last_modified": "2025-07-01T04:22:28.334080",
    "storage_policy": "Policy-0"
  },
  {
    "name": "user-data",
    "count": 0,
    "bytes": 0,
    "last_modified": "2025-07-01T04:22:07.707130",
    "storage_policy": "Policy-0"
  }
]

Notes:
At 09:43:27 UTC the attacker queried the Swift storage root: GET /v1/AUTH_9fb84977ff7c4a0baf0d5dbb57e235c7?format=json
The 376-byte JSON response revealed 3 containers:
- dev-files → empty, never accessed
- employee-data → exfiltrated at 09:45:47 UTC
- user-data → exfiltrated at 09:45:23 UTC
Q10 — When did the attacker download the sensitive user data file? (UTC)
Answer 2025-07-01 09:45:23
_path=="http"
| id.orig_h == 117.200.21.26
| "user-data"
| cut ts, method,id.orig_h, uri, response_body_len
| sort ts

Notes
Filtered HTTP traffic from attacker IP 117.200.21.26 for all requests targeting the user-data container. The download was identified by the GET request with a non-zero response body:
Q11 — How many user records are in the sensitive user data file?
Answer 28
cat user-details.csv | wc -l  → 29 lines
29 - 1 (header) = 28 user records
Notes
Exported user-details.csv from the PCAP using wireshark.
Counted rows excluding the header line:
Q12 — For persistence, the attacker created a new user with admin privileges. What is the username of the new user?
Answer
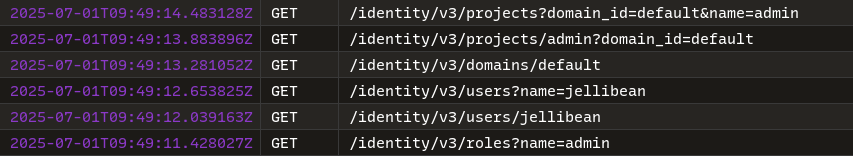
$ grep -r "jellibean"
users(1):{"user": {"password": "P@$$word", "enabled": true, "default_project_id": "9fb84977ff7c4a0baf0d5dbb57e235c7", "name": "jellibean"}}
users(2):{"user": {"id": "c373da67a62b48f393c45dc071fa80b8", "name": "jellibean", "domain_id": "default", "enabled": true,
"default_project_id": "9fb84977ff7c4a0baf0d5dbb57e235c7", "password_expires_at": null, "options": {},
 "links": {"self": "http://134.209.71.220/identity/v3/users/c373da67a62b48f393c45dc071fa80b8"}}}
Notes
Ran grep -r "jellibean" against all HTTP objects extracted from controller.pcap. Found the user creation POST request body confirming username jellibean with default_project_id matching the admin project.
Q13 — What is the password of the new user?
Answer P@$$word
Notes
Password found in the same POST /identity/v3/users request body extracted in Q12. Plaintext credentials in API traffic confirm no encryption was used on the internal network (HTTP not HTTPS).