RogueOne Sherlock Walkthrough
Volatility 3 memory forensics on a masquerading svchost.exe C2 implant: process analysis, executable dumping, MD5 extraction and attack timeline reconstruction.
Solved RogueOne from Hack The Box!
Attack Timeline
| Timestamp (UTC) | Event | Evidence Source |
|---|---|---|
| 2023-08-10 11:30:03 | Malicious svchost.exe (PID 6812) executed from C:\Users\simon.stark\Downloads\ and C2 channel established to 13.127.155.166:8888 |
windows.netscan, windows.cmdline |
| 2023-08-10 11:30:57 | cmd.exe (PID 4364) spawned by malicious process for interactive command execution |
windows.pstree |
| 2023-08-10 11:30:57 | conhost.exe (PID 9204) spawned automatically by cmd.exe |
windows.pstree |
| 2023-08-10 ~11:30+ | SIEM generates multiple C2 communication alerts | Scenario description |
| 2023-08-10 11:58:10 | Malware sample first submitted to VirusTotal by reverse engineering team | VirusTotal |
Key observation: The entire attack — from initial execution to active C2 communication to interactive shell access — took less than 1 minute. This indicates an automated implant with pre-configured C2 callback, not manual exploitation.
Scenario: Your SIEM system generated multiple alerts in less than a minute, indicating potential C2 communication from Simon Stark’s workstation. Despite Simon not noticing anything unusual, the IT team had him share screenshots of his task manager to check for any unusual processes. No suspicious processes were found, yet alerts about C2 communications persisted. The SOC manager then directed the immediate containment of the workstation and a memory dump for analysis. As a memory forensics expert, you are tasked with assisting the SOC team at Forela to investigate and resolve this urgent incident.
Tools used: Volatility 3, strings/grep
Q1 — Please identify the malicious process and confirm process id of malicious process.
Answer: 6812
We used the windows.cmdline plugin to list all running processes along with their full command-line paths:
$ vol3 -f 20230810.mem windows.cmdline

Key indicators:
- PID 6812 is running
svchost.exe— a legitimate Windows process name - However, the path is
C:\Users\simon.stark\Downloads\svchost.exeinstead of the expectedC:\Windows\System32\svchost.exe - This is a classic masquerading technique (MITRE T1036.005) — the attacker named the malicious binary after a legitimate system process to blend in
- This also explains why Simon’s Task Manager didn’t raise suspicion — the process name appeared normal
Q2 — The SOC team believe the malicious process may spawned another process which enabled threat actor to execute commands. What is the process ID of that child process?
Answer: 4364
We used the windows.pstree plugin filtered by the malicious PID to view its child processes:
$ vol3 -f 20230810.mem windows.pstree --pid 6812

Key indicators:
- PID 4364 —
cmd.exewith PPID 6812 (our malicioussvchost.exe) — this is the child process the threat actor used to execute commands - PID 9204 —
conhost.exewith PPID 4364 — this is the Console Window Host automatically spawned bycmd.exe, which is expected behavior - Both processes were created at 2023-08-10 11:30:57 UTC, the same timestamp — indicating
cmd.exewas spawned immediately by the C2 implant - A C2 agent spawning
cmd.exeis a common post-exploitation pattern for interactive command execution
Q3 — The reverse engineering team need the malicious file sample to analyze. Your SOC manager instructed you to find the hash of the file and then forward the sample to reverse engineering team. Whats the md5 hash of the malicious file?
Answer: 5bd547c6f5bfc4858fe62c8867acfbb5
We used the windows.dumpfiles plugin to extract the malicious binary from memory, then hashed it:
$ vol3 -f 20230810.mem windows.dumpfiles --pid 6812
$ md5sum file.0x9e8b91ec0140.0x9e8b957f24c0.ImageSectionObject.svchost.exe.img
5bd547c6f5bfc4858fe62c8867acfbb5

Key indicators:
- The
--pid 6812flag dumps all files associated with the malicious process, including loaded DLLs and the main executable - We hash the ImageSectionObject (
svchost.exe.img), not the DataSectionObject (svchost.exe.dat) — the ImageSectionObject represents the actual PE executable as loaded into memory, which is the closest to the original binary on disk - The DataSectionObject is a data-level file mapping used for caching and may be incomplete or modified
Q4 — In order to find the scope of the incident, the SOC manager has deployed a threat hunting team to sweep across the environment for any indicator of compromise. It would be a great help to the team if you are able to confirm the C2 IP address and ports so our team can utilise these in their sweep.
Answer: 13.127.155.166:8888
We used the windows.netscan plugin to extract network connections and filtered for the malicious PID:
$ vol3 -f 20230810.mem windows.netscan > exported_files/netscan.txt
$ cat netscan.txt | grep 6812

Key indicators:
- PID 6812 (
svchost.exe) has an ESTABLISHED TCP connection to 13.127.155.166 on port 8888 - The local machine IP is 172.17.79.131 using ephemeral port 64254
- Port 8888 is a common port used by C2 frameworks (e.g., Metasploit, Cobalt Strike, custom implants)
- The connection was established at 2023-08-10 11:30:03 UTC — this timestamp helps establish the initial compromise timeline
- The 13.127.x.x range belongs to AWS ap-south-1 (Mumbai), which could indicate attacker-controlled cloud infrastructure
Q5 — We need a timeline to help us scope out the incident and help the wider DFIR team to perform root cause analysis. Can you confirm time the process was executed and C2 channel was established?
Answer: 10/08/2023 11:30:03
The answer was already visible from the netscan output used in Q4:
$ cat netscan.txt | grep 6812

Key indicators:
- The netscan output shows the C2 connection was ESTABLISHED at 2023-08-10 11:30:03 UTC
- This timestamp represents when the malicious
svchost.exe(PID 6812) first connected to the C2 server at13.127.155.166:8888 - This correlates with the SIEM alerts that triggered the investigation
- Note: the
cmd.exechild process (PID 4364) was spawned at 11:30:57 UTC — roughly 54 seconds after the C2 channel was established, suggesting the attacker took nearly a minute to begin interactive command execution
Q6 — What is the memory offset of the malicious process?
Answer: 0x9e8b87762080
We used the previously exported windows.pslist output and filtered for the malicious PID:
$ cat exported_files/psslist.txt | grep 6812

Key indicators:
- The Offset(V) column shows the virtual memory address of the process’s
EPROCESSstructure - PID 6812 (
svchost.exe) resides at offset 0x9e8b87762080 - This offset can be used to manually inspect the process’s kernel structure in memory, or as input for other Volatility plugins that accept a virtual offset (e.g.,
--offset)
Q7 — You successfully analyzed a memory dump and received praise from your manager. The following day, your manager requests an update on the malicious file. You check VirusTotal and find that the file has already been uploaded, likely by the reverse engineering team. Your task is to determine when the sample was first submitted to VirusTotal.
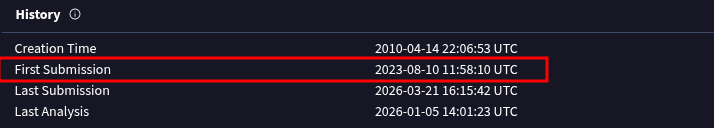
Answer: 10/08/2023 11:58:10
We searched the MD5 hash 5bd547c6f5bfc4858fe62c8867acfbb5 on VirusTotal and checked the Details tab under the History section:
Key indicators:
- First Submission shows 2023-08-10 11:58:10 UTC — this is when the reverse engineering team uploaded the sample
- This is only ~28 minutes after the C2 channel was established (11:30:03 UTC), showing a fast incident response turnaround
- The Creation Time of 2010-04-14 22:06:53 UTC is likely a falsified PE timestamp — attackers often forge compilation timestamps to mislead analysts (a technique known as
timestomping)