Lupin Sherlock Walkthrough
Reversing a stealthy Windows dropper with Cutter and diec: entropy analysis, masquerading filename, locale-based execution checks and C2 cache-evasion techniques.
Scenario
After a security incident, unusual activity on Samira’s workstation led to the discovery of a suspicious binary operating stealthily in the background. The executable evades standard detection while maintaining persistence and network communication. Your mission is to reverse the binary and extract the attacker’s TTPs for the endpoint security team.
| Field | Value |
|---|---|
| Category | Malware Analysis |
| Difficulty | Medium |
| Status | InProgress |
| Date | |
| Artifacts | Malicious executable optimize.exe |
| Tools | diec |
Q1 — What is the entropy value of the executable file?
Answer 6.41450
To determine whether the binary was packed or obfuscated, we calculated its entropy using diec with the -e (entropy) flag. Entropy measures randomness in a file’s byte distribution — values above 7.0 typically indicate packing or encryption, while values below that suggest readable, unobfuscated content.
$ diec -e optimize.exe
Total 6.4145: not packed
  0|PE Header|0|1024|2.29117: not packed
  1|Section(0)['.text']|1024|59392|6.11097: not packed
  2|Section(1)['.rdata']|60416|14336|5.60578: not packed
  3|Section(2)['.data']|74752|7168|5.67993: not packed
The overall entropy of 6.4145 falls below the packing threshold, and diec confirms not packed across all sections. The .text section (executable code) sits at 6.11097, consistent with compiled native code. No section shows suspiciously high entropy, meaning the binary is unlikely to be compressed or encrypted — we can proceed with static analysis directly.
Q2 — What is the consistent filename used by the malware when replicating itself across different locations?
Answer syscrondvr.exe
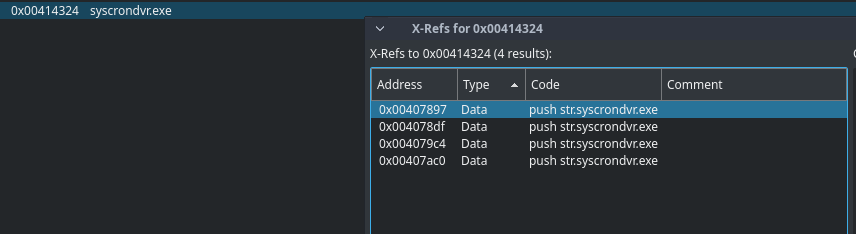
Since the binary is a native C PE, we opened it in Cutter and searched for CreateFileW — the Windows API used to create or open files. To find what filename is passed to it, we searched all strings in the binary and identified syscrondvr.exe as a candidate. Cross-referencing it via X-Refs revealed 4 separate call sites all pushing str.syscrondvr.exe as an argument, confirming this is the hardcoded filename the malware consistently uses when copying itself to different locations. The code preview also shows calls to GetModuleFileNameW, PathFindFileNameW, and ExpandEnvironmentStringsW nearby — indicating the malware resolves target paths dynamically before dropping the copy.
MITRE ATT&CK:
T1036.005— Masquerading: Match Legitimate Name or Location (filename mimics a legitimate-sounding system driver service)
Q3 — Following filename verification, which Win32 API does the binary use to enforce region-based execution constraints?
Answer GetLocaleInfoA
After identifying the self-replication filename in the previous step, we continued static analysis in Cutter by searching the strings panel for locale-related keywords. Searching for local surfaced GetLocaleInfoA in the binary’s referenced strings — a Win32 API used to retrieve locale information for a given locale identifier. Its presence indicates the malware performs a region check at runtime, likely comparing the system’s locale against a hardcoded target value and altering execution behavior (continuing, exiting, or sleeping) based on the result.
Also can use strings
strings optimize.exe| grep -i 'locale'
GetLocaleInfoA
MITRE ATT&CK:
T1614.001— System Location Discovery: System Language Discovery (adversaries query locale/language settings to determine whether they are operating in a targeted or safe region)
Q4 — The function at relative address 0x407680 makes a WinAPI call immediately before initiating the network request. Which WinAPI function does it call to ensure fresh data is retrieved from the C2 server?
Answer DeleteUrlCacheEntry
We navigated directly to address 0x407680 in Cutter and scrolled through the function body. The function opens with two nested loops calling Sleep(1000ms) — an evasion technique to outlast sandbox timeouts. It then dynamically constructs a C2 URL using wsprintfA with a format string and domain values pulled from a hardcoded array at 0x414310. Immediately before the network request is initiated, the malware calls DeleteUrlCacheEntry on the freshly built URL, purging any cached response from the Windows Internet cache and forcing a live fetch from the C2 server.
0x00407757 call dword [wsprintfA] ; build C2 URL string 0x00407767 call dword [DeleteUrlCacheEntry] ; purge cache before fetch
MITRE ATT&CK:
T1071.001— Application Layer Protocol: Web Protocols (C2 communication over HTTP) |T1497.003— Virtualization/Sandbox Evasion: Time Based Evasion (Sleeploops to evade sandbox analysis)
Q5 — Samira noticed unusual behavior during the paste operation — what is the relative address of the function that is responsible for this strange activity?
Answer