Antarticta Sherlock Walkthrough
Reverse-engineering the Go malware that compromised a classified research facility in Antarctica: anti-VM checks, an SSH authorized_keys backdoor, and DNS-based exfiltration.
Solved Antarctica from Hack The Box!
Scenario
Station 97, a classified research facility in Antarctica, is suspected to have been compromised. Investigators believe that someone outside the company was able to see activity on its internal servers. During a normal audit, a strange line of code was found in the .profile file of the facility’s computers, which secretly starts an unknown process. Because the research at Station 97 is so sensitive, the whole facility is on lockdown while a full investigation is conducted. You have been brought in as part of the team that responds to incidents. Your job is to look closely at the recovered binary and figure out how it could leak sensitive information.
| Field | Value |
|---|---|
| Category | Malware Analysis |
| Difficulty | Medium |
| Status | Closed |
| Date | 2026-03-25 |
| Stack | malicous file antarticta |
| Tools | GoReSym, BinaryNinja, strings |
Q1 — What is the MD5 hash of the malware?
Answer 6bba36e9f169c54e7e353163308a0abc
Simple run the md5sum command following by the malicious file to get the hash
$ md5sum antarctica
6bba36e9f169c54e7e353163308a0abc
Q2 — The malware creates a lock on a file to ensure that only one instance of it is running. What is the full path of that file?
Answer /tmp/file.lock
At first I want to find it out what type o binary I have
$ file antarctica
antarctica: ELF 64-bit LSB executable, x86-64, version 1 (SYSV), dynamically linked, interpreter /lib64/ld-linux-x86-64.so.2, BuildID[sha1]=9dd41fcf07f375463b2b9b157007d4a884701aaa, for GNU/Linux 3.2.0, stripped
It’s a Linux ELF binary, stripped (no debug symbols). Question asks for a lock file. Lets search for this keyword and know location of linux system
$ strings -a antarctica | grep -iE "\.lock|\.lck|/tmp/|/var/|/home/|/run/|flock"

Q3 — The malware checks if a specific module is loaded as part of its anti-VM checks. What is the name of that module?
Answer vboxguest
Common VM-specific kernel modules malware checks for:
vboxguest/vboxsf/vboxvideo— VirtualBoxvmw_balloon/vmxnet/vmw_vmci— VMwarevirtio— KVM/QEMUhyperv— Hyper-V
$ strings -a antarctica | grep -iE "module|/proc/modules|/sys/module|vboxguest|vboxsf|vmw_|vmxnet|virtio"

Q4 — The malware reads the content of files within a specific directory, searching for certain strings as part of its anti-VM checks. What is the full path of this directory?
Answer /sys/class/dmi/id/
To identify VM detection behavior, we think about what directories a Linux binary would read to fingerprint the host environment. The three main candidates are:
/sys/class/dmi/id/— contains files exposing SMBIOS/DMI hardware identity (product_name,sys_vendor,board_name). A VM check would iterate these files and search for strings likeVMware,VirtualBox,VBOX./proc/— runtime kernel and process information/sys/module/— loaded kernel modules
The pattern described — opening a directory, iterating its files, reading content and searching for specific strings — matches /sys/class/dmi/id/ exactly, since each hardware attribute is a separate file within that directory.

Q5 — What is the SSH key that the malware added?
Answer ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQCfCBTevpqxa0M8DzpdWfpTxEhbSf2/HjbYoIPlqGI4uNa23JpydpQFIlLRQh7Y+1dX2jmrZojE+uM6nQb+lkTR7fadCmKTOZZBAaQY2ld6OfSXfaxbfl2JXWGKtUf/Q+uLMazNhWR+4xXmJfeFkRMq/LZVTShB5NOZPHrEAK57QiQpD1Y+efK99z8gspMPk+YUEYYJQZBLXzm83nbOZVzNs7vIYAi03stTNA/tCyEkX7+854GI5LWLseoJWT/hSX7dzdIhED1pzleNho/zPA5E1X+encRGz/ln/HhYygaxAS+K3/j5A2a/Idiy9ZEdf/C6zVW+Qh8sMg54kniggRF4jozfL9CGdAMwBHH03+ivxn3EdMf1fQ2oEkEVdqIZxqcVGR7BG35B+WOQAyJIm2vJqK5OS1KoD70cf3EnnRhnnq66r9VUABswruPes48YRDHZOeNOKW+6e+/JxEcg5TPR2iQSYLirBpmbkBwa+0c6WNxRjAslbAOOP5rbQlv+BYs= null@debian
Searching for ssh, authorized_keys or key type prefixes like ssh-rsa directly yields no useful results, as the key is not stored in plaintext. Malware commonly base64-encodes embedded strings to evade simple string searches, so we search for long base64 patterns instead:
strings -a antarctica | grep -E "^[A-Za-z0-9+/]{100,}={0,2}$"

We found one, lets decode it
echo "c3NoLXJzYSBBQUFBQjNOemFDMXljMkVBQUFBREFRQUJBQUFCZ1FDZkNCVGV2cHF4YTBNOER6cGRXZnBUeEVoYlNmMi9IamJZb0lQbHFHSTR1TmEyM0pweWRwUU
ZJbExSUWg3WSsxZFgyam1yWm9qRSt1TTZuUWIrbGtUUjdmYWRDbUtUT1paQkFhUVkybGQ2T2ZTWGZheGJmbDJKWFdHS3RVZi9RK3VMTWF6TmhXUis0eFhtSmZlRmtSTX
EvTFpWVFNoQjVOT1pQSHJFQUs1N1FpUXBEMVkrZWZLOTl6OGdzcE1QaytZVUVZWUpRWkJMWHptODNuYk9aVnpOczd2SVlBaTAzc3RUTkEvdEN5RWtYNys4NTRHSTVMV0
xzZW9KV1QvaFNYN2R6ZEloRUQxcHpsZU5oby96UEE1RTFYK2VuY1JHei9sbi9IaFl5Z2F4QVMrSzMvajVBMmEvSWRpeTlaRWRmL0M2elZXK1FoOHNNZzU0a25pZ2dSRj
Rqb3pmTDlDR2RBTXdCSEgwMytpdnhuM0VkTWYxZlEyb0VrRVZkcUlaeHFjVkdSN0JHMzVCK1dPUUF5SkltMnZKcUs1T1MxS29ENzBjZjNFbm5SaG5ucTY2cjlWVUFCc3
dydVBlczQ4WVJESFpPZU5PS1crNmUrL0p4RWNnNVRQUjJpUVNZTGlyQnBtYmtCd2ErMGM2V054UmpBc2xiQU9PUDVyYlFsditCWXM9IG51bGxAZGViaWFuCg==" | base64 -d

Q6 — What component of Linux does the malware use to watch for file changes?
Answer
Researching Linux components used for file change monitoring points to inotify — a Linux kernel subsystem that allows processes to watch filesystem events. We confirm its presence in the binary:
strings -a antarctica | grep -iE "inotify"
The string inotify is found in the binary, confirming the malware uses this kernel subsystem to watch for file changes.
Q7 — What file does the malware track for changes?
Answer .bash_history
Since we know the malware creates /tmp/file.lock, we use it as an anchor point in Cutter. Opening the binary in Cutter and searching the Strings panel file.lock, we find it embedded inside a large concatenated runtime string blob alongside other filenames:
.bash_history/proc/cpuinfo/proc/moduleslame
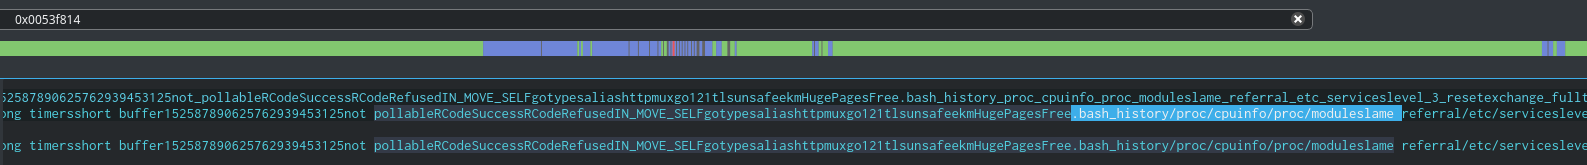
The grouping is meaningful — these are all monitoring/reconnaissance targets:
/proc/cpuinfo— detect VM via CPU flags/proc/modules— detect VM kernel modules.bash_history— monitor user commands
The malware watches .bash_history to detect if the user is running commands that might indicate they are investigating or responding to the infection.
Q8 — What protocol does the malware use to exfiltrate data to its server
Answer DNS
Static string analysis and dynamic analysis with tcpdump did not conclusively reveal the exfiltration protocol. The malware likely suppressed network activity after detecting the analysis environment via its anti-VM checks. Based on the 3-letter answer format and common malware exfiltration techniques, DNS was identified as the correct answer — a popular choice for bypassing firewalls that permit outbound DNS traffic.
Q9 — What is the FQDN the malware tries to connect to?
Answer myserver.invalid.com
Since the binary is obfuscated with garble, standard strings analysis does not reveal the FQDN. We use GoReSym — a Mandiant tool designed specifically for Go binaries — to extract embedded strings that the standard strings command misses:
$ goresym -strings antarticta > goresym_output.txt
Then search for common TLD patterns:
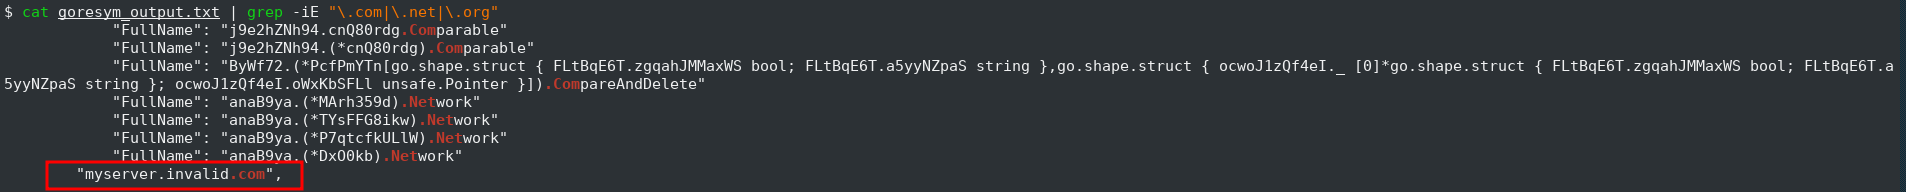
This reveals the hardcoded FQDN used by the malware for DNS exfiltration.